

tldr;
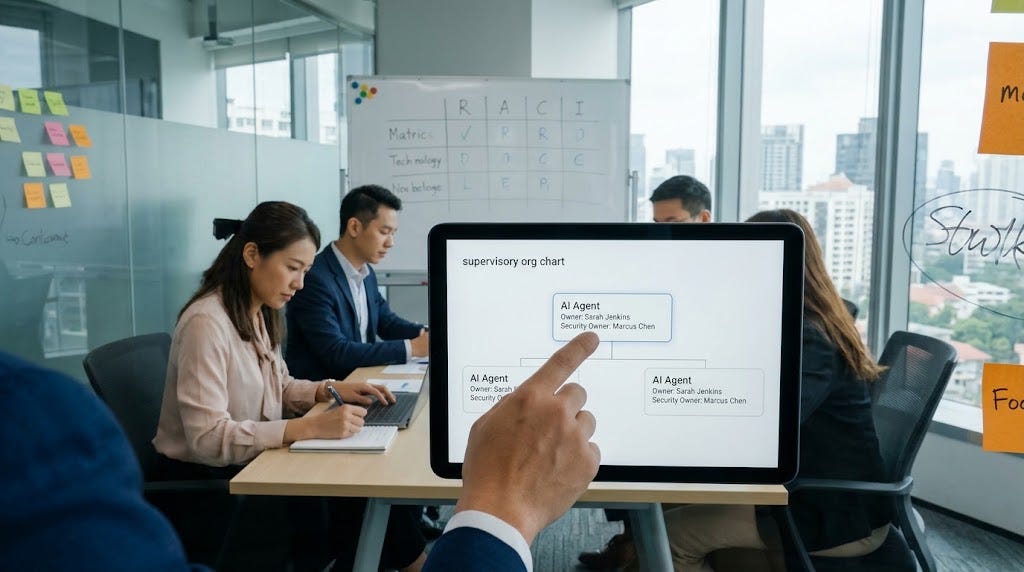
AI agents now show up in your supervisory org chart. Workday’s Agent Owners feature (in production since Oct 23, 2026R2) lets you put named humans on every agent. Workday’s framing: a business owner who owns the cost center the agent bills to, and a technical owner who owns its configuration. The roles themselves are yours to define.
That’s a better ownership model than most tenants run for their integration system users. That should sting a little.
It’s setup-required, so it does nothing until you build it. Two ways this fails: nobody sets it up, or the owner field gets filled in by whoever happened to be in the activation meeting.
Monday homework: stand up the owner roles, build a two-column RACI, trim the agent’s tool list, then run the same two columns against your ISUs.
The demo agent at the Extend session had a name, a security group, an execution mode, and fourteen tools. One of those tools was find performance review.
The agent’s job was to recommend internal job reqs. Nobody on stage explained why it needed to read performance reviews. To be fair, nobody in the audience asked either. We were all watching the progress spinner. (It ran for about eight minutes and still wasn’t done. Live demos remain undefeated.)
What I actually wrote in my notes was a different question: whose direct report is this thing?
As of this fall, that’s a literal question. Agents now appear in the supervisory org chart, and each agent owner is tied to an organization. There is now a security domain called, and I promise I’m not making this up, View: Agents in Org Chart. Every agent has its own identity, its own account, and its own security group. It has a desk now.
So somebody has to manage it.
What Workday actually built
Credit where it’s due: Workday did more of the org design here than most HR teams have done for their own automations.
Agent Owners. Live in production as of Oct 23 (2026R2), and it’s setup-required, so it does nothing until you build it. You define the owner roles yourself (Workday’s examples are Business Partner and Technical Partner), assign them per agent, and scope what each role can see or do for that agent only. Workday’s blog describes the intended split: a business owner “who uses the agent to drive value and owns the cost center it bills to,” and a technical owner “responsible for its configuration and support” (Workday, Oct 14). (The release note calls the setup domain Setup: Agent Org and Owners in one paragraph and Setup: Agent Org and Support Owners in the next. Even the governance feature has a labeling problem.)
Agent Passport. Early access now, with GA planned for year end. A “stamp” answers three questions about an agent: what was it tested for, who tested it, and against which standard. Cisco AI Defense runs the adversarial testing on every agent Workday builds. Straiker and OneTrust plan to join as assessors. An agent with no stamp can still run if you allow it, and Workday’s own post says that in that case you’re trusting it blind.
C1.ai. Workday is acquiring C1.ai for identity governance, meaning provisioning, access reviews, and de-provisioning for both employees and agents. The deal is expected to close by the end of Workday’s fiscal year in January.
One more detail: registering an agent in the Agent System of Record requires the UMSA. If you read last week’s issue, that was three of the twelve tables at the Share-a-thon.
We never did this for our ISUs
Pull up your integration system users. Go ahead, I’ll wait.
How many of them have a named business owner? How many have a cost center? How many have security scoped to exactly what that integration needs, instead of a group someone cloned from another ISU in 2019 because go-live was Friday?
In most tenants I’ve seen (mine included, at various points in my career), the honest answers are: a few, none, and please don’t make me look.
ISUs were the original agents. They’re non-human accounts acting in your tenant, with permissions, on a schedule, for fifteen years now, and the ownership model behind them has mostly been a naming convention and hope. Somewhere in your tenant is an ISU whose owner left before the pandemic, and the integration still runs every night at 2 AM because nobody wants to find out what happens if it doesn’t.
Workday’s release note explains why Agent Owners exists: the old model was all-or-nothing, people supporting agents “end up with far more access than they need,” and that’s “a segregation-of-duties problem.” They were writing about agents. They could have been writing about half the ISUs in the ecosystem.
So my first reaction is respect.
My second reaction is the Bus Factor post. A field that holds a name is only as good as the habit that keeps that name current.
Two rows, two kinds of accountability
Agents run in two modes, and your RACI needs a row for each.
Delegate. The agent acts for the person who asked. It can never do more than that person can do, and it can’t raise its own privileges. That’s the mode the Extend demo agent ran in. Accountability splits cleanly: the requester owns the ask, and the technical owner owns what the agent is able to reach.
Ambient. The agent acts as itself. Workday’s documentation describes this mode, but per Incubane’s session notes, a fully autonomous agent running on a schedule is still on the roadmap. So for now this row is empty. When it fills, there’s no requester at all. The business owner becomes the only human in the sentence.
Build both rows now, while one of them is still empty. It’s much easier to staff a row before the agent starts filling it.
Where it breaks
Two ways, and the first one is quieter.
Setup-required features have a way of staying not configured. Agent Owners needs an assignable role, a role-based constrained security group, and domain policy changes before it does anything. In a lot of tenants that will land on the backlog right behind the last three setup-required features, and the agents will go live under the old all-or-nothing model anyway.
The second way is worse because it looks like success. The owner field gets filled in the activation meeting by whoever is in the room. Probably the HRIS lead (hi) as technical owner, and whichever director sponsored the business case as business owner. Then that director takes a new job. The field still has their name in it. The agent keeps billing to a cost center whose new leader has never heard of it, and the first time anyone reads the usage report is at renewal.
Last week’s Share-a-thon table already described this pattern: AI councils approve an agent once and never look at it again. An owner field filled in at approval time is that same gate with a name tag on it.
Monday homework
Crawl. Turn it on. Run Maintain Assignable Roles and create a role enabled for Agent Management. Create a role-based constrained security group for it. Attach that group to the agent domain policies, then activate pending security policy changes. Before the first activation, build a two-column RACI for each agent: the person who owns the cost center, and the person who owns the security group. Names, not titles. A backup name in each column.
Walk. Open the tool list on every agent you’re testing and remove anything the agent’s job doesn’t require. If a talent advisor genuinely needs performance reviews, someone should be able to explain why in one sentence. If nobody can, the tool goes.
Run. Apply the same two columns to your ISUs. You’ll find the ones nobody owns, and you’ll find them before an agent that depends on them does. Then add a to-do to your termination and job change business processes that reminds the manager to reassign any agents the worker owns. Five minutes of configuration now will save you a scavenger hunt in 2028.
I’ve put this on one page:

Forward it to InfoSec and Procurement before your first agent goes live.
Workday gave the agent a desk. Put a name on the chair.
— Mike Director HR Tech | Manager of Record, One New Direct Report
The Department of First Things First. For the people who do the work.
P.S. I asked Justin who owns what in the Lab. He didn’t look up from his dinner: he owns all five printers, the queue, and the pricing. I own “IT,” which he defined as fixing the AMS when it jams and not touching the queue. Mom has slightly more responsibility than me. So that’s one proprietor, five machines working shifts, and two technicians whose access is scoped and who can’t raise their own privileges. It’s a cleaner owner model than most tenants have. I checked.
P.P.S. To my friends in Dallas: last Monday night, at the Linc, 38 to 21. Your Cowboys walked into my house and did whatever they wanted to my team that’s now essentially running in preseason mode. That’s not Schattenfreude (stay tuned for what that means). That’s the regular, full-strength German kind, and you’ve earned every syllable. (Six losses in a row (thanks Washington), for anyone keeping score in Texas. I know you are.) But here’s the twist: I grew up rooting for a crappy team. I’ll still be here after this season. We’re resilient and scrappy in Philly. Plus we have LeBron so there’s something else to focus on. Enjoy it. See you on Thanksgiving. Go Birds.